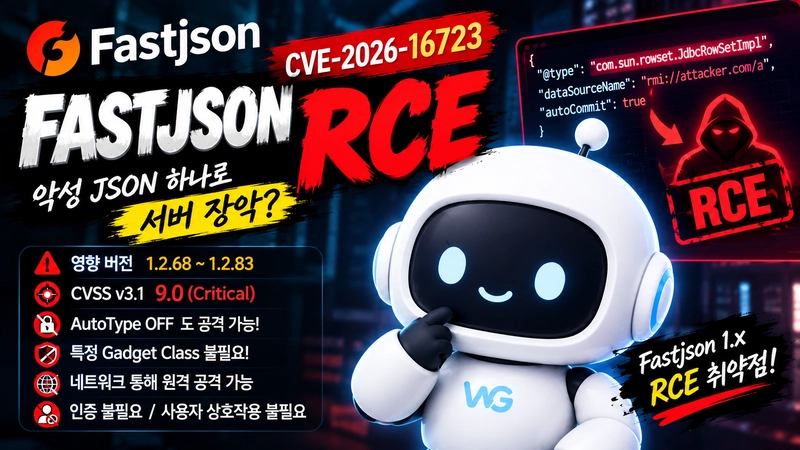

The enterprise Java ecosystem is confronting a severe security crisis following the disclosure of a critical remote code execution (RCE) vulnerability, tracked as CVE-2026-16723, affecting legacy versions of Alibaba’s Fastjson library. Assigned a maximum CVSS severity score of 9.0 to 9.8 depending on the scoring authority, the vulnerability allows unauthenticated attackers to achieve complete system compromise without relying on traditional gadget classes or bypassing explicit AutoType protection mechanisms. The discovery has sent shockwaves through the cybersecurity community, primarily because it impacts applications running Fastjson versions 1.2.68 through 1.2.83, a legacy branch that remains deeply embedded in thousands of enterprise production environments despite the software reaching end-of-life status.
Background Context and the Legacy Fastjson Problem
Fastjson has a long and turbulent history regarding deserialization vulnerabilities. Since the initial wave of exploits began around CVE-2017-18349, Alibaba and security researchers have engaged in a multi-year game of cat-and-mouse. Over six distinct rounds of defensive hardening were introduced to secure Fastjson’s ParserConfig.checkAutoType() method. These iterative patches included the deployment of denylists, the implementation of FNV-1a rolling hashes, the introduction of a global safeMode kill switch, and tightening constraints around expected classes.
By the time version 1.2.83 was released, the parser’s validation routine was widely considered one of the most thoroughly scrutinized and heavily audited pieces of code in the Java ecosystem. However, these historic patches shared a fundamental design flaw: they focused exclusively on determining whether a class name specified in the JSON @type attribute matched a known dangerous gadget class, such as JdbcRowSetImpl or FileSystemXmlApplicationContext.

CVE-2026-16723 bypasses these rigorous checks entirely by exploiting an entirely different code path—specifically, the metadata verification branch associated with the @JSONType annotation. Because developers historically trusted metadata annotations as internal developer-controlled declarations, this code path was never treated as untrusted input surface area.
Detailed Attack Chain and Mechanics
The vulnerability functions through a deterministic, six-step attack chain that requires no memory corruption, race conditions, or probabilistic timing. Attackers can trigger the exploit pre-authentication simply by submitting a maliciously crafted JSON payload to any endpoint that utilizes an insecure Fastjson configuration.
When the parser encounters an arbitrary type string, it passes through initial name-shape filters like safeMode and hash-based denylists. Because an attacker-controlled string formatted for remote resource retrieval does not resemble a traditional Java class name, it easily evades these basic filters.
The core vulnerability activates within the metadata inspection logic. Fastjson attempts to determine whether a class possesses the @JSONType annotation. To do this, it converts the dotted package notation of the string into a slash-separated resource path and queries the default class loader via getResourceAsStream().

In standard Spring Boot deployments configured with an executable fat-JAR, the default class loader is LaunchedURLClassLoader, which subclasses URLClassLoader. Crucially, this class loader natively supports the jar:http:// URL scheme. Upon receiving the request, the class loader opens an outbound HTTP connection to a remote server hosted by the attacker, downloads the raw class bytes, and passes them to ASM’s ClassReader for static parsing. While ASM safely parses the bytecode without executing it, the act of fetching the class bytes establishes the external connection.
Once the parser detects the presence of the @JSONType annotation—which can easily be embedded into a custom, attacker-compiled class—Fastjson marks the type as safe and proceeds to invoke TypeUtils.loadClass(). This triggers the Java Virtual Machine to formally load the class via defineClass(). Under standard JVM specifications, the moment a class is prepared for use, its static initializer (<clinit>) block executes precisely once.
The attacker’s custom class contains a static initializer block pre-programmed to execute operating system commands, such as downloading and executing a secondary payload via shell utilities. Consequently, the attacker does not need to instantiate the class, invoke any methods, or interact with the returned Class<?> object. Merely forcing the JVM to load the remote class completes the remote code execution chain.
Overcoming Technical Hurdles: Integer-IP Encoding
A significant technical obstacle traditionally faced by attackers exploiting Java class loaders via URL schemes is Fastjson’s internal string transformation logic. During the initial parsing phase, Fastjson replaces all dots (.) with forward slashes (/) to construct valid internal resource paths. If an attacker were to supply a standard IPv4 address such as 192.168.1.100 within the URI, the transformation logic would convert the dots into slashes, resulting in a malformed and broken URL.

To circumvent this restriction, sophisticated threat actors employ 32-bit integer IP encoding. By converting the IPv4 address into its equivalent 32-bit integer representation—for example, transforming 192.168.1.100 into 3232235876—the string contains no literal dots. The integer passes through Fastjson’s string replacement untouched. When the underlying java.net.URL class subsequently opens the socket, it automatically decodes the integer back into the correct dotted IP address, successfully establishing communication with the remote server.
Chronology of Disclosures and Official Responses
The discovery of CVE-2026-16723 highlights the systemic risks associated with unmaintained open-source software dependencies. Alibaba officially declared the Fastjson 1.x branch as End-of-Life (EOL) long before this vulnerability was discovered, actively directing developers to migrate entirely to Fastjson2.
Because Fastjson 1.x is officially deprecated, the maintainers have confirmed that no official patch will be released for the vulnerable 1.x codebase. Organizations relying on software packages built on Fastjson 1.2.68 through 1.2.83 are left entirely without a vendor-supplied update.
In response to the disclosure, independent security researchers, enterprise vulnerability management teams, and cloud security providers have scrambled to issue guidance and detection signatures. Industry bodies have rated the vulnerability with a CVSS score of up to 9.8, reflecting the trivial nature of exploitation and the widespread presence of vulnerable dependencies in containerized microservices and enterprise applications.

Broader Impact and Implications for Enterprise Security
The emergence of CVE-2026-16723 underscores several critical architectural risks in modern application development:
- The Danger of Deprecated Dependencies: Millions of applications worldwide still incorporate unpatched, EOL software libraries because upgrading requires substantial code refactoring. Vulnerabilities like this demonstrate that legacy libraries can harbor fundamental design flaws that remain dormant for years.
- Limitations of Denylists and Hardening: Iterative patching of complex parsers often fails when underlying assumptions about metadata and class loading are flawed. Fixing deserialization vulnerabilities by adding more items to a denylist or validating specific string shapes is proven to be an unsustainable defensive strategy.
- Network Segmentation and Egress Filtering: In many environments, the impact of CVE-2026-16723 is magnified by permissive cloud network policies. If compromised JVM instances are permitted unrestricted outbound internet access, attackers can easily fetch remote payloads. Strict egress filtering serves as a vital compensating control, disrupting the first stage of the remote fetch chain.
Actionable Mitigations and Workarounds
Since upgrading Fastjson 1.x is not an option, security teams must implement alternative risk-reduction strategies to protect vulnerable systems:
- Enable Global Safe Mode: The most robust workaround is activating Fastjson’s
safeModeby supplying the JVM startup argument-Dfastjson.parser.safeMode=true. This forcescheckAutoType()to throw an exception unconditionally at the very beginning of execution, blocking the entire attack path. However, this measure will break applications that legitimately rely on polymorphic deserialization via@typeannotations. - Transition to Fastjson2: Organizations should prioritize migrating their codebases to Fastjson2. The successor library was architecturally redesigned from the ground up, utilizing an explicit allowlist approach for trusted types before interacting with class loaders, thereby eliminating this class of vulnerability entirely.
- Restrict Outbound Network Traffic: Implementing strict firewall rules and egress filtering on application servers prevents the JVM from resolving external
jar:http://orjar:https://requests, neutralizing the remote fetch primitive even if the application processes malicious JSON payloads. - WAF and Runtime Application Self-Protection (RASP): Deploying signature-based rules at the web application firewall level can help detect anomalous payloads attempting to inject complex URI schemes into serialization attributes, though security teams should note that URL encoding obfuscation can occasionally bypass superficial regex filters.
As threat actors begin scanning public-facing endpoints for unpatched Fastjson implementations, organizations must urgently audit their dependency trees, inventory legacy Java applications, and apply comprehensive network-level mitigations to prevent catastrophic system compromises.